The Johns Hopkins Breach Wasn’t Brought on by a Hacker. It Began With 1 Worker Add

One employee’s mistake exposed sensitive medical information belonging to 3,182 patients and revealed a growing security risk for every workplace.

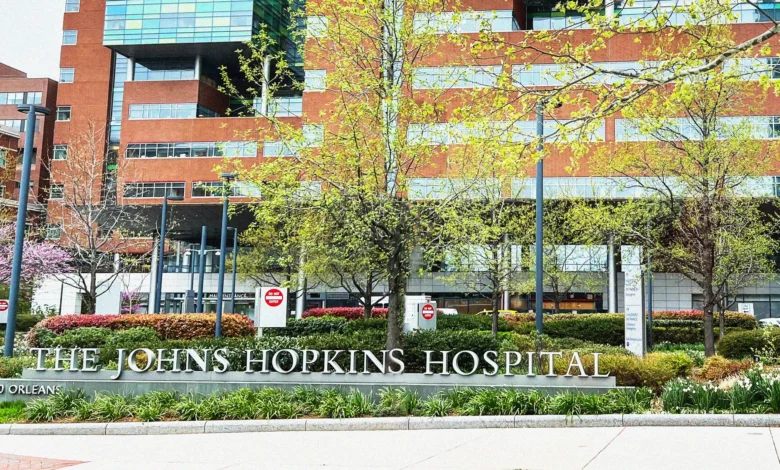
More than 3,000 patients at the Johns Hopkins Bayview Medical Center had their medical information shared with an unauthorized artificial intelligence in a major data breach. The incident occurred in September when an employee uploaded a spreadsheet with the health data of 3,182 people to an undisclosed public AI tool that the hospital had not approved for usage.
As reported by the Baltimore Banner, while the data did not include Social Security numbers or financial information, it did include detailed medical information including the patient’s doctors, medications, and treatment history. Johns Hopkins has asked the AI’s parent company to delete the confidential data and has notified all affected patients of the breach.
Johns Hopkins is committed to maintaining the privacy
“Johns Hopkins is committed to maintaining the privacy and security of its patients’ information and is taking this incident very seriously,” read a press release from Johns Hopkins. “We sincerely regret any inconvenience or concern this may have caused.”
Johns Hopkins is not the first workplace to struggle with workers using AI in unauthorized and harmful ways. Several years ago, Samsung had a similar incident where an employee accidentally leaked the company’st contractor shared with ChatGPT a file containing the personal information of thousands of recent flood victims
The daily digest for entrepreneurs and business leaders
These cases are examples of a larger phenomenon haunting the workplace: shadow AI usage. Shadow AI refers to when employees use AI tools that have not been approved by their company. In a report from IBM that studied 600 organizations that had data breaches, 20 percent had data breaches caused by shadow AI usage. These incidents were also more likely to mistakenly reveal customer’s personal information and cost an average of $670k more to resolve.
According to law firm Falcon Rappaport & Berkman,
According to law firm Falcon Rappaport & Berkman, shadow AI usage can open up companies to serious liabilities under HIPAA and other privacy laws. That confidential data is now out of the workplace’s control, and exists on another company’s server where it is vulnerable to being viewed without proper authorization.
“When your health record leaves the hospital system, it’s losing a lot of the protections that would otherwise apply under federal law,” said Harvard law professor I. Glen Cohen in an interview with Harvard Law Todaydiscussing the risks of uploading health data to an AI LLM. “Once exposed, your health information could be used in all sorts of ways.”
Source: www.inc.com